Permissions, Governance and Configuration
Centralize permissions, governance, and configuration to control access, enforce policies, and ensure consistent system behavior across the organization.
Configuration Foundations
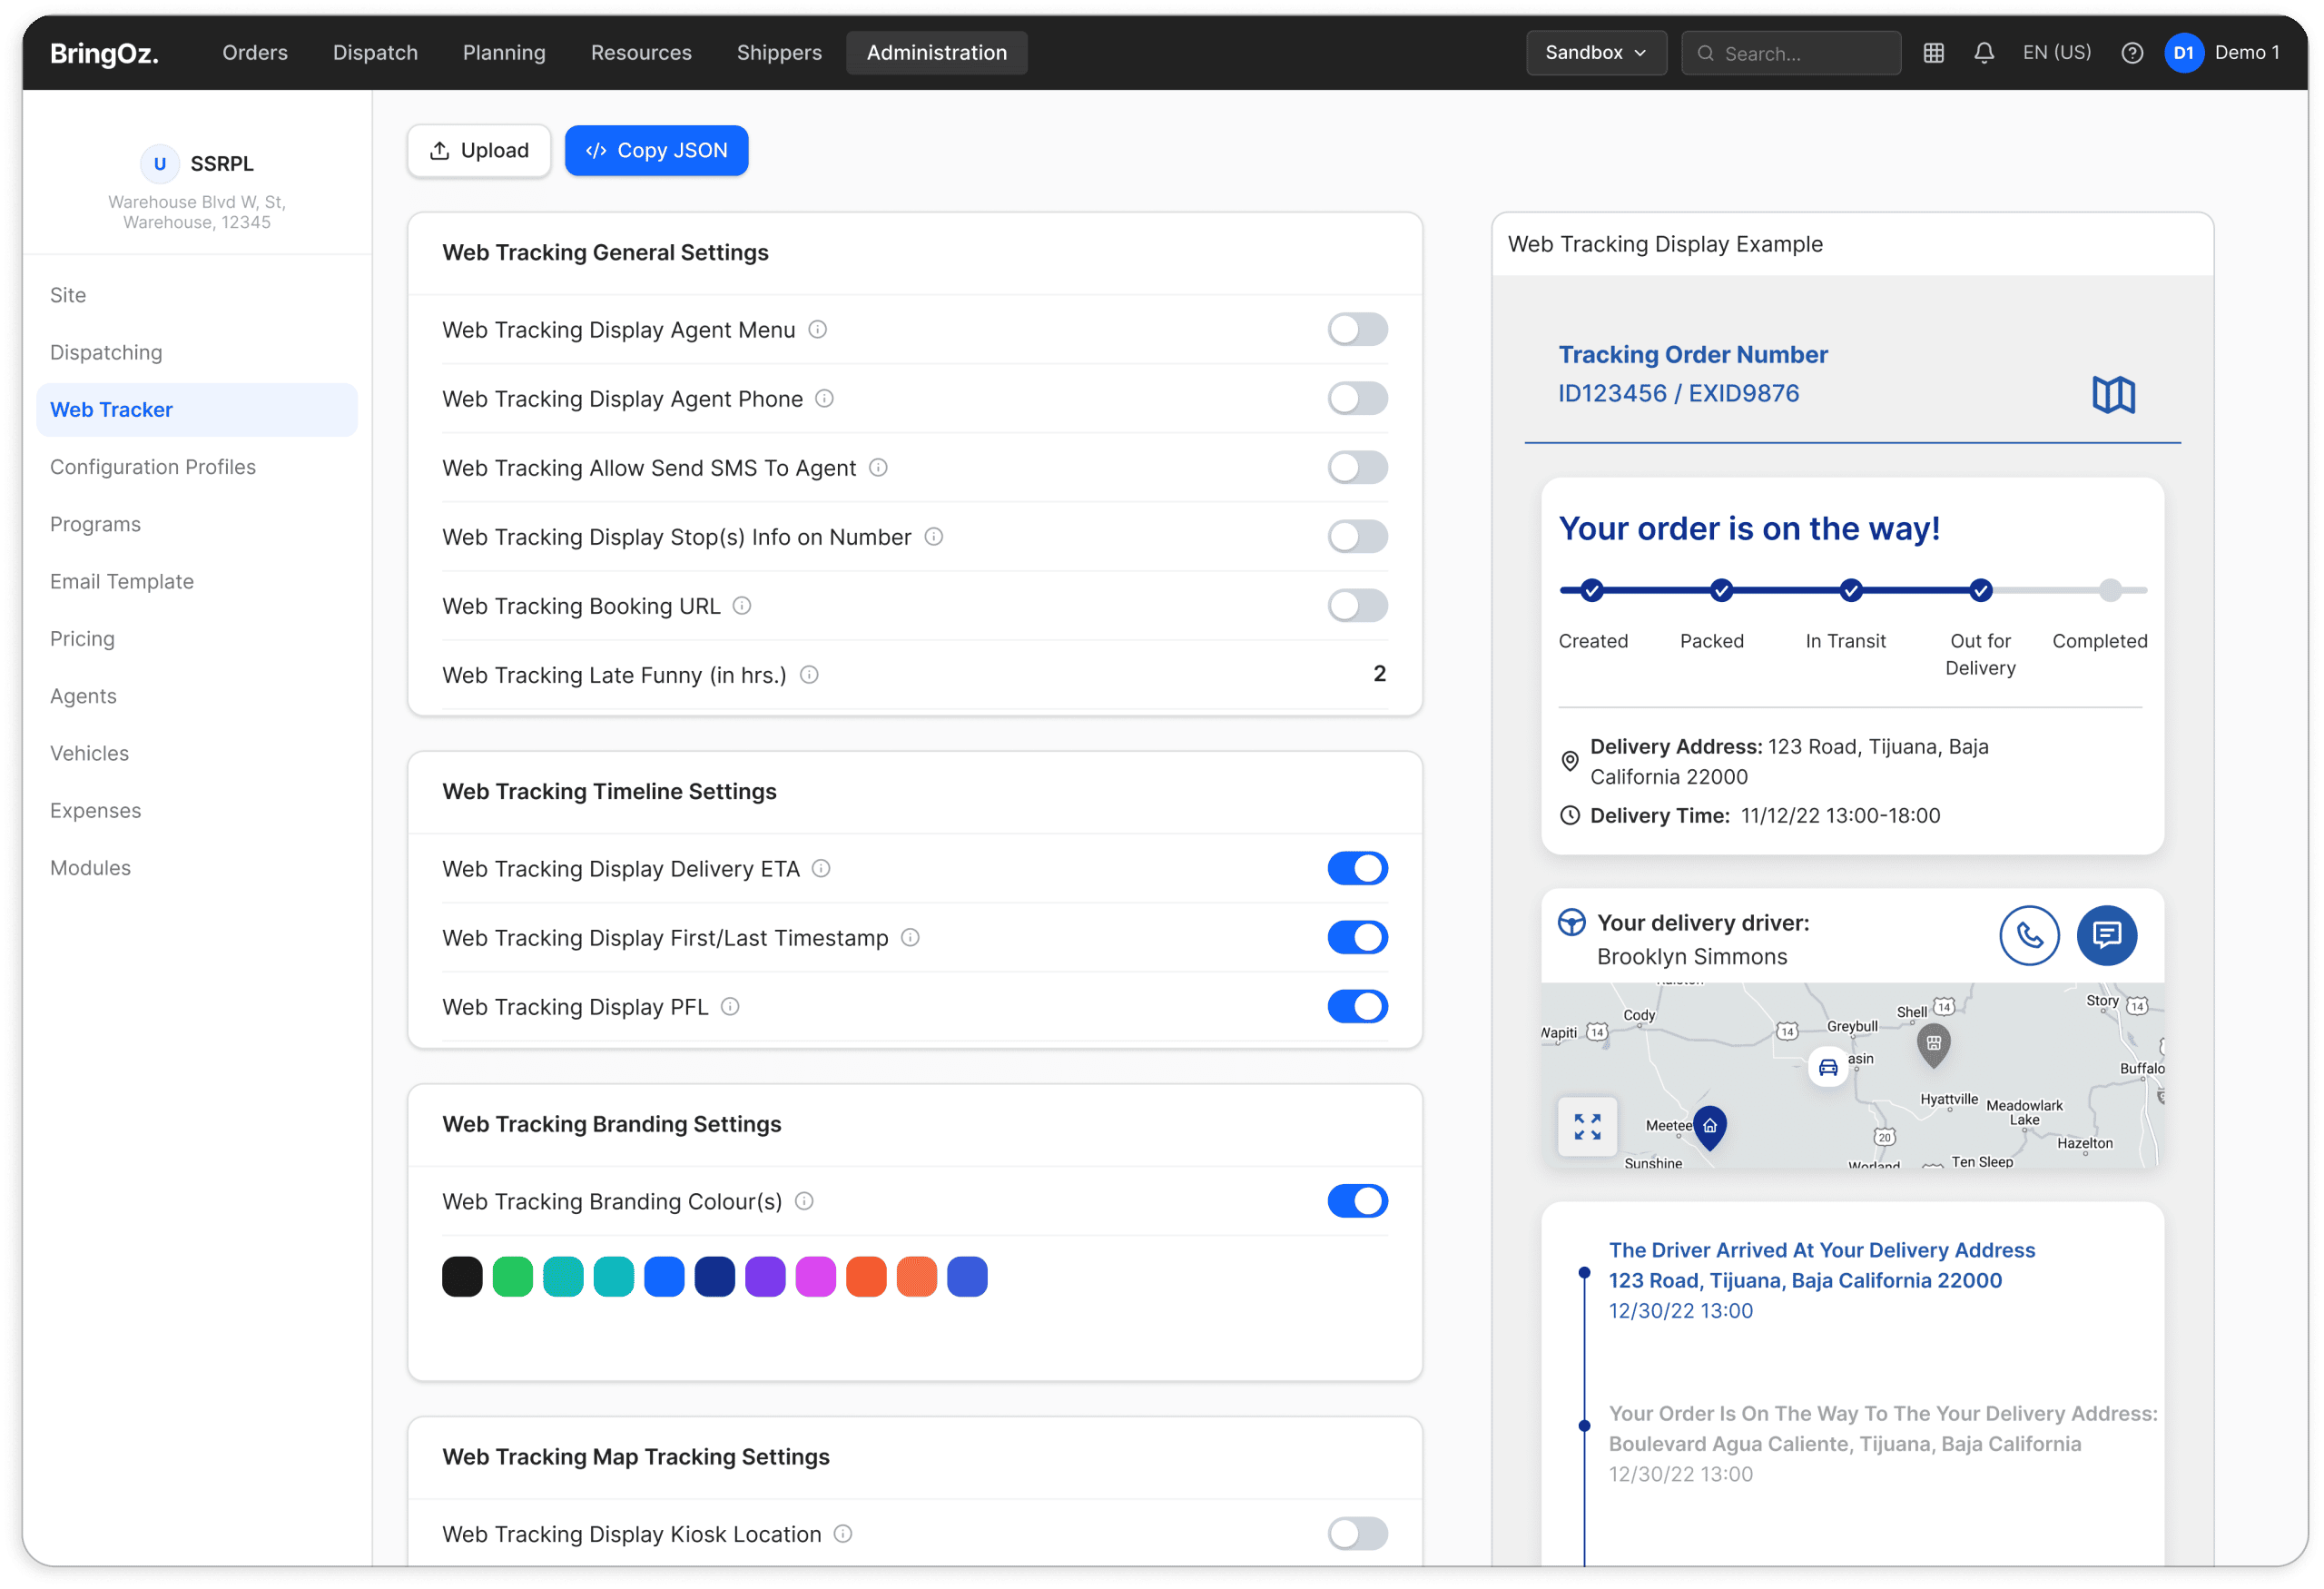
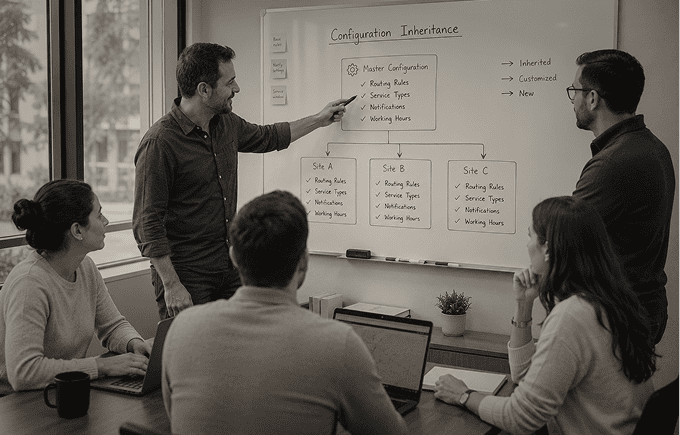
Central Framework
Single control layer governing platform behavior.
Entity Configuration
Configure behavior by customer, region, or entity type.
Hierarchical Defaults & Overrides
Inherit settings with controlled overrides.
Effective Date Configuration & Management
Schedule configuration changes over time.
Planning, Scheduling & Execution Configuration
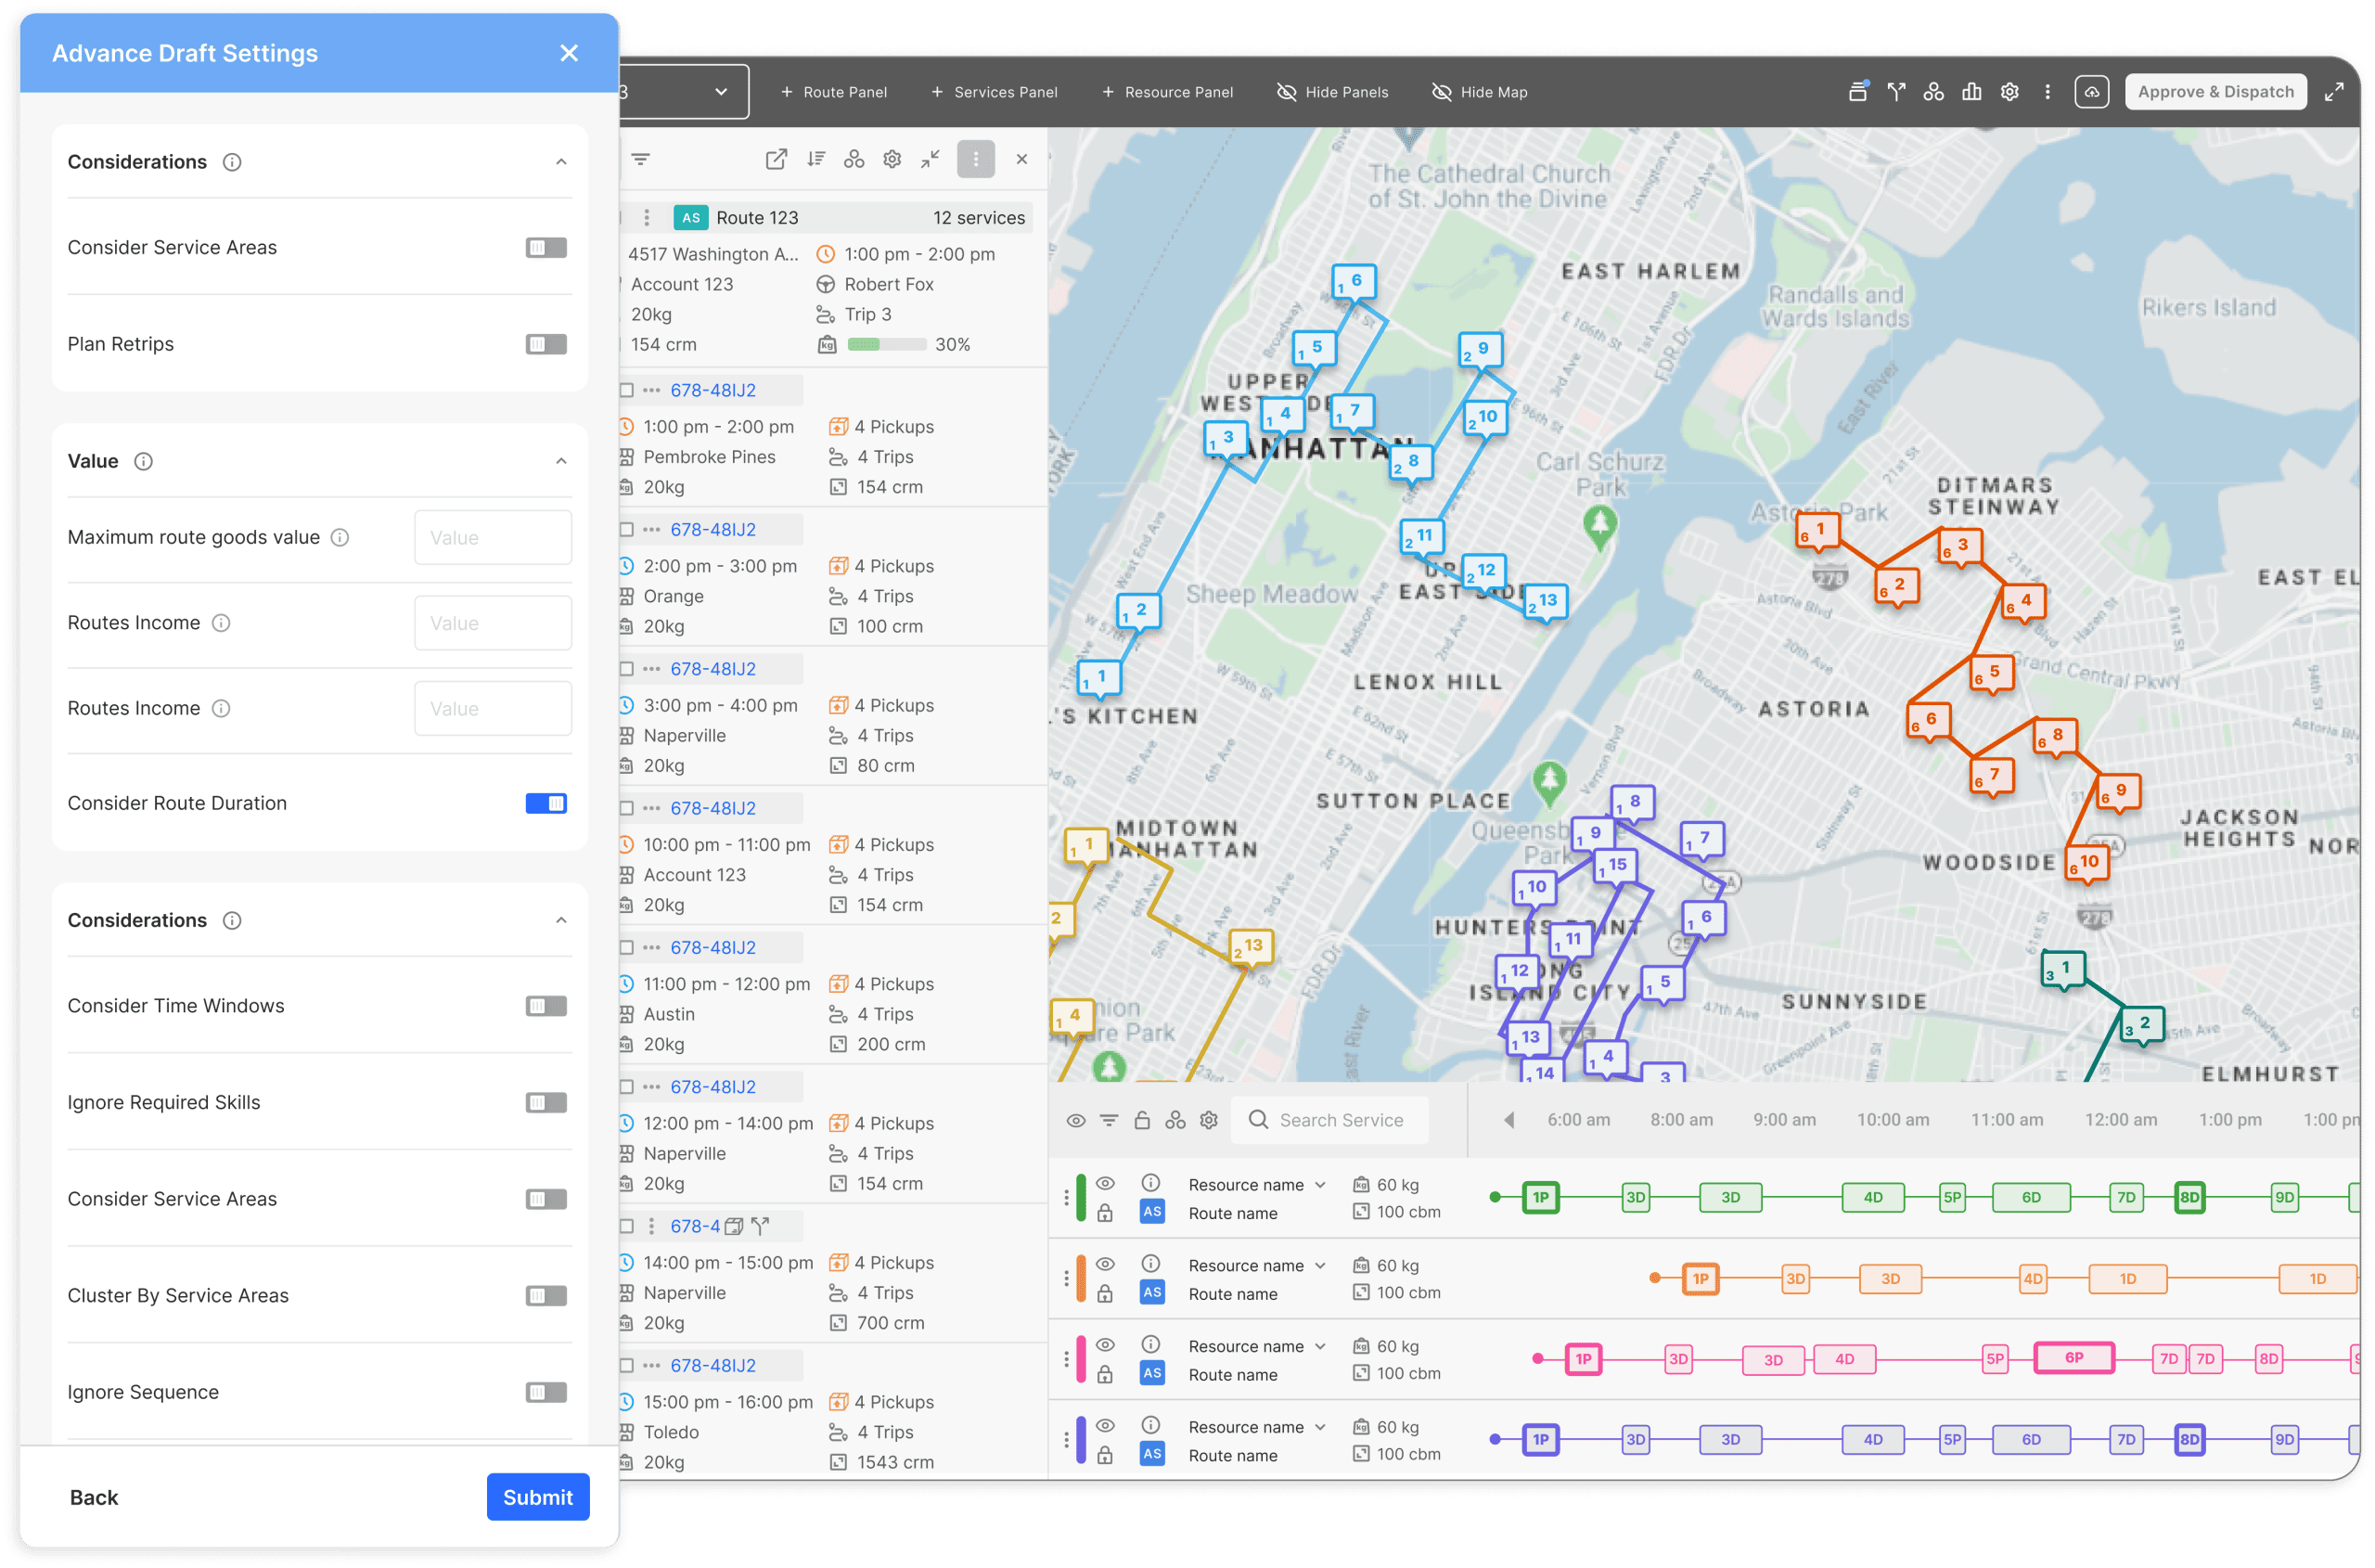
Planning & Scheduling Parameters
Configure planning logic, priorities, and constraints.
Routing & Optimization Rules
Define routing behavior and optimization parameters.
Execution Workflow Configuration
Control execution steps, validations, and workflows.
Rescheduling & Replanning Policies
Define how plans adapt to changes.
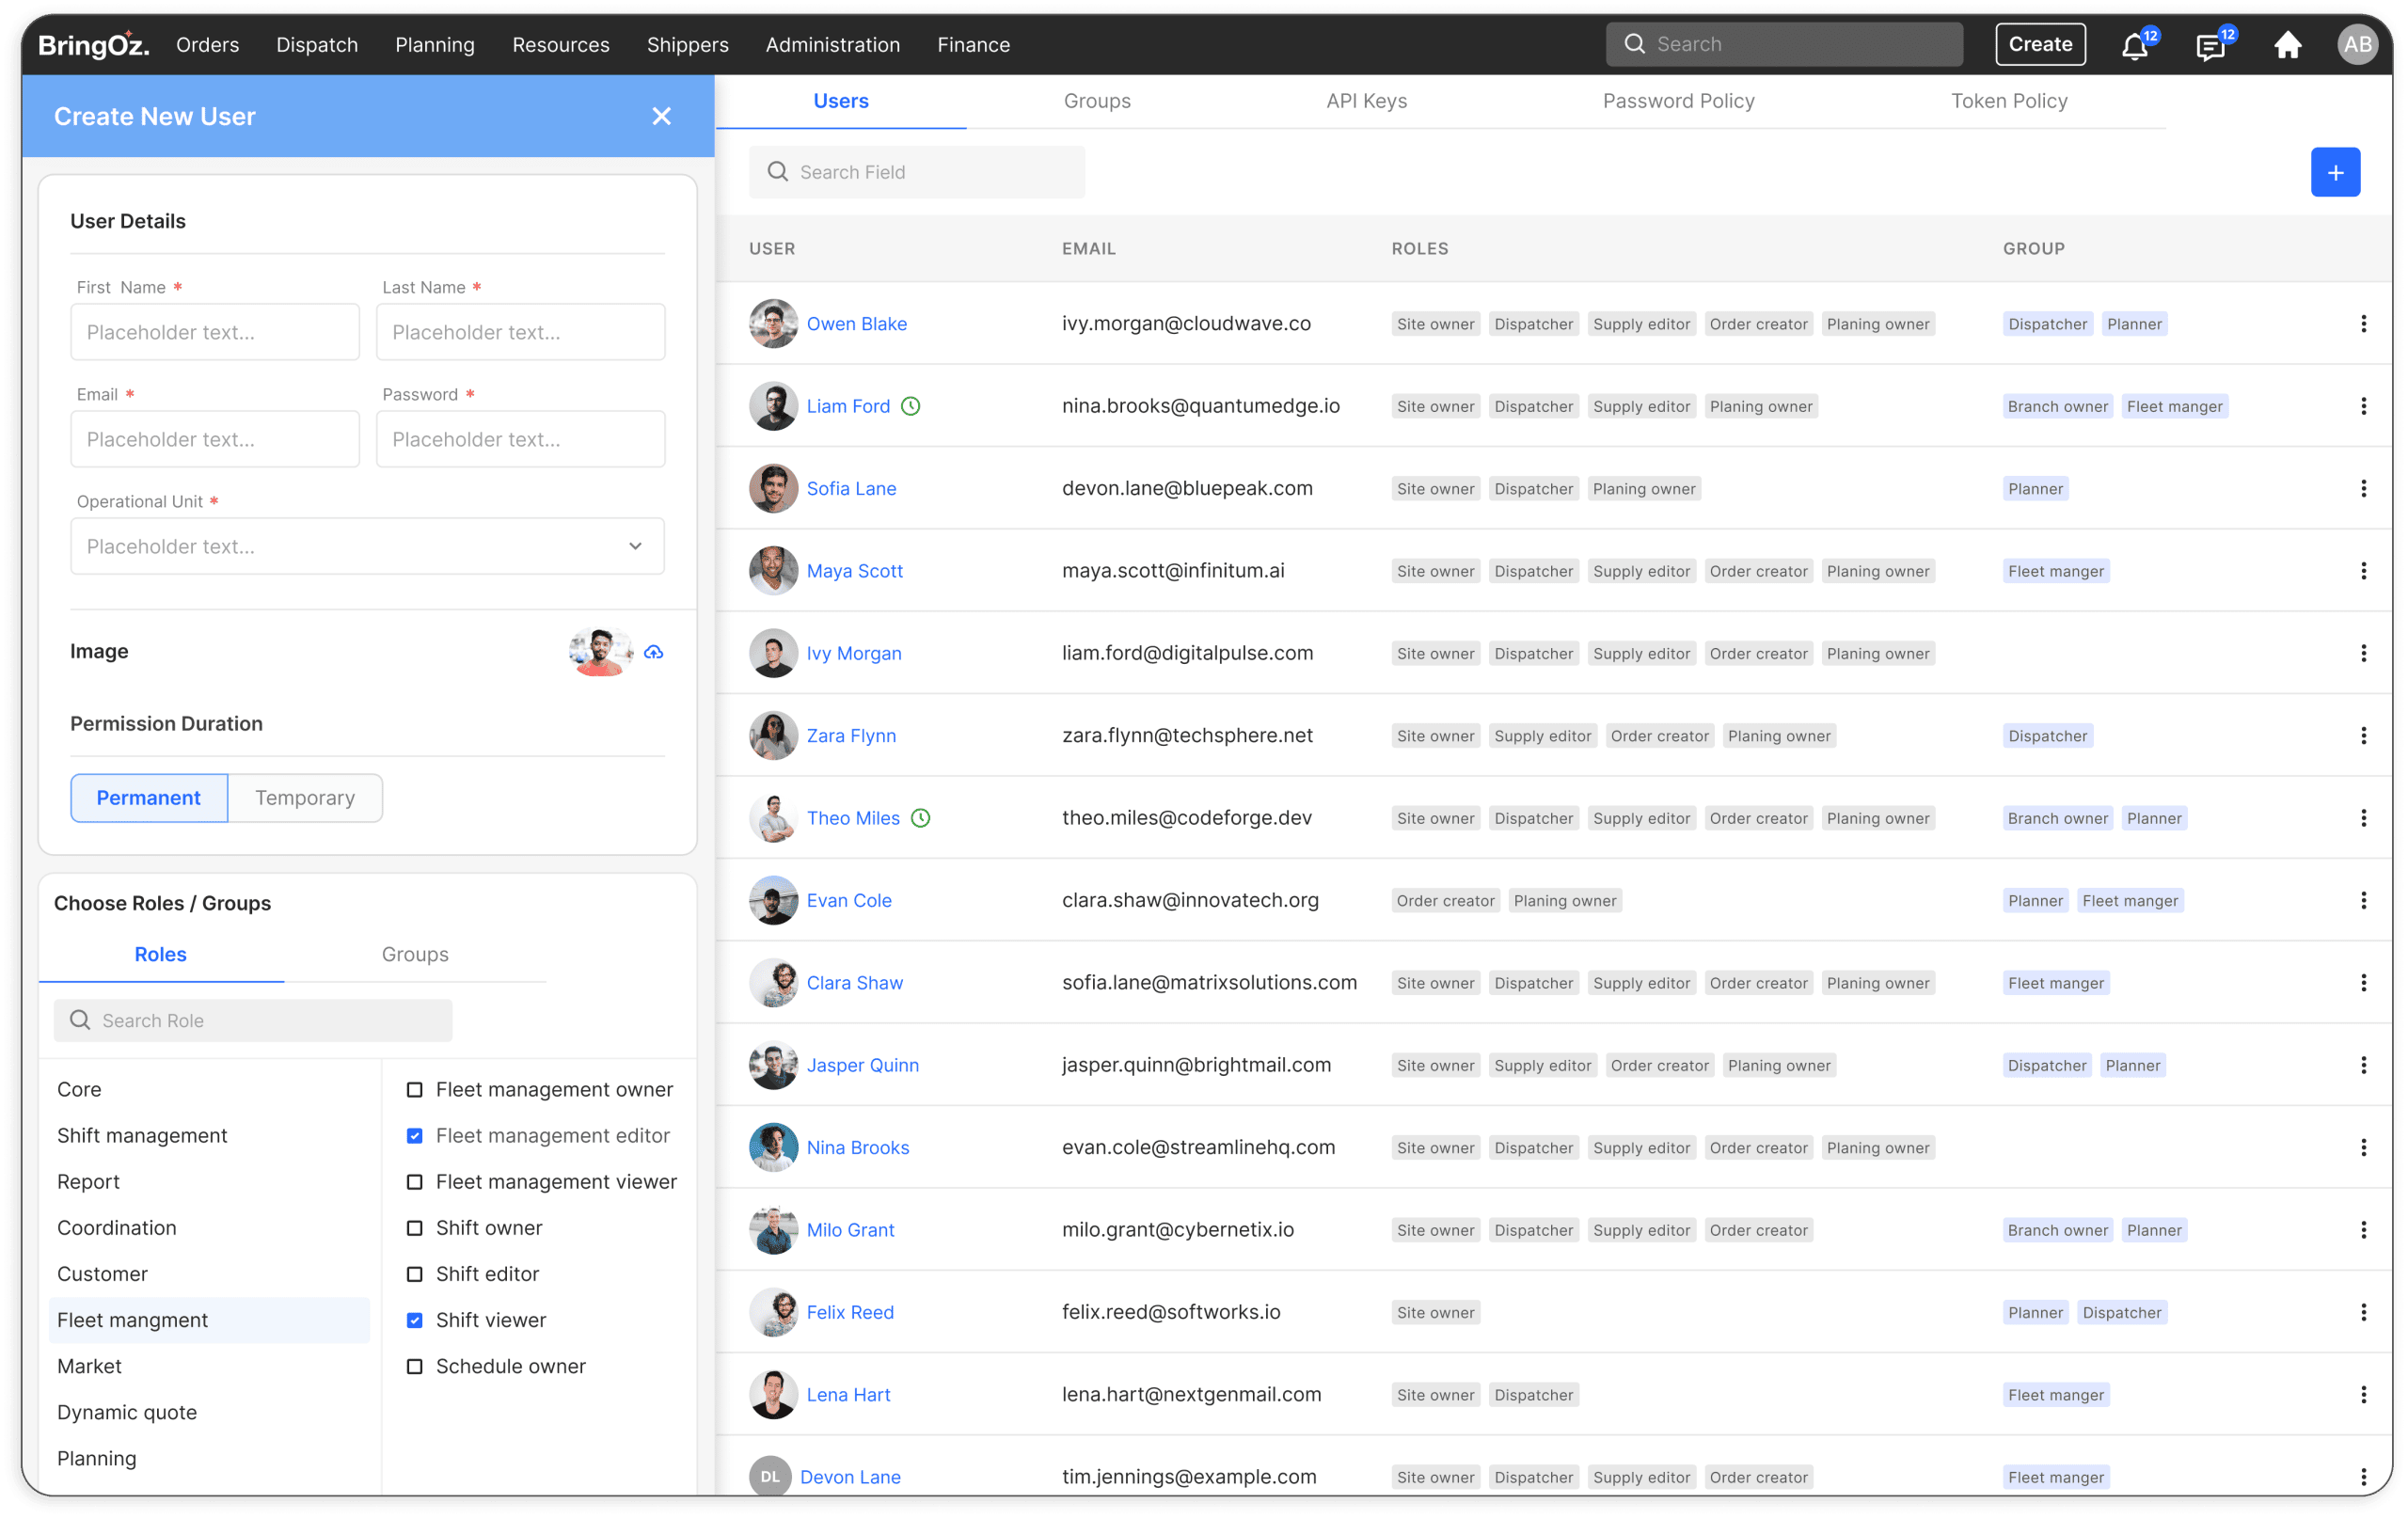
User, Role & Access Configuration
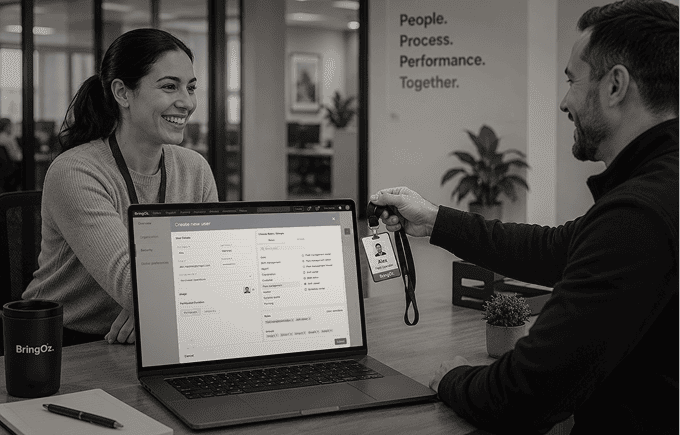
Role-Based Configuration Access
Control system configuration access by role and responsibility.
User-Level Configuration Overrides
Apply specific configuration overrides for individual users when needed.
Approval-Based Configuration Changes
Enforce approvals for sensitive configuration changes.
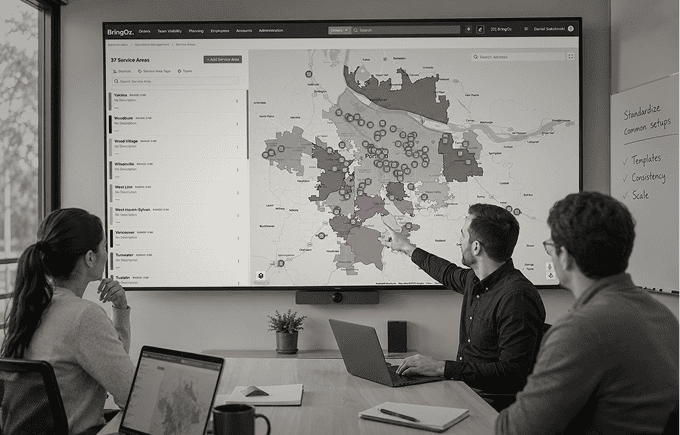
Organizational & Regional Segmentation
Segment access and configuration by organization, region, or unit.
Analytics & Optimization Configuration
KPI & Metric Configuration
Define KPIs, thresholds, and measurement logic.
Alert & Notification Configuration
Configure alerts, triggers, and notification channels.
Optimization Objectives
Set and tune optimization goals and trade-offs.
AI Model & Signal Tuning
Control AI inputs, weights, and constraints.
FAQs
BringOz uses roles, permissions, organizational structures, rules, and workflows to control who can view, change, approve, and execute work.
Yes. Permissions can be configured by organizational level, territory, team, role, function, or other operational scope.
Yes. Central policies can coexist with regional or local configuration where operational flexibility is required.
Actions, changes, approvals, and key operational decisions can be recorded through audit trails for traceability.
Yes. Governance rules and workflows can require specific approvals, validations, or actions before work proceeds.
BringOz can use connected data and workflows to support consistent operational controls across the broader technology ecosystem.
Standardized structures and controls help organizations maintain consistency as regions, teams, workflows, and volumes expand.
Yes. Override rights can be limited to authorized roles and managed through configurable permissions and governance policies.
Enterprise security, role-based access, data controls, and auditability help protect operational information.
It improves accountability, consistency, compliance, control, and confidence across complex enterprise operations.
Curious about
pricing?
BringOz pricing depends on several factors. To provide an accurate quote, please complete the form and we’ll connect you with the right expert shortly.